How does changing DKIM selectors impact email reputation and what are the best practices for key rotation?
Updated on 19 Oct 2026: We updated our DKIM rotation guidance with sourced retention advice, provider-managed selector safeguards, and checks for post-rotation failures.
Changing a DKIM selector usually does not cause a major reputation reset by itself. The selector is a lookup label for the public key, not the main identity behind the mail stream. Receivers care more about the signing domain, visible From domain, sending IP, mail quality, complaints, bounces, engagement, and whether authentication satisfies DMARC.
Receiver reputation models are proprietary, so a selector change cannot guarantee identical filtering decisions. A new selector is still a routine part of secure key rotation, but unnecessary selector churn makes changes harder to diagnose. Rotate for a defined security, vendor, or lifecycle reason, then monitor the cutover.
The safest method is simple: publish a new selector with a new public key, confirm it is resolvable, start signing with the matching private key, keep the old selector published while delayed mail clears, then retire the old key. For active senders, changing the selector is safer than overwriting the key behind the same selector.
Does changing a DKIM selector affect reputation?
A DKIM selector change has low direct reputation risk when the new selector validates, the same signing domain is used, the From domain relationship still satisfies DMARC, and mail volume stays stable. The bigger risk is a broken DNS record, missing public key, signing mismatch, alignment change, or early deletion of the old selector.
A selector appears in the s= tag of the DKIM signature. With s=2026a and d=example.com, the receiver checks the public key at 2026a._domainkey.example.com. Verification also requires a valid signature over the signed message content.
Changing only the selector does not require a new domain or IP warm-up. DMARC checks the DKIM signing domain against the visible From domain under its strict or relaxed alignment mode, not the selector name. A selector-only rotation does not require a DMARC record change.
- Reputation: A selector-only change generally preserves the signing identity when the domain and sending IP stay the same.
- Authentication: Broken DKIM can hurt DMARC results if SPF cannot provide the required aligned pass.
- Security: Rotating keys limits exposure from old private keys, vendor turnover, poor storage, and historical leakage.
- Timing: Keep the old selector live long enough for queued, retried, forwarded, or deferred-verification mail to validate.
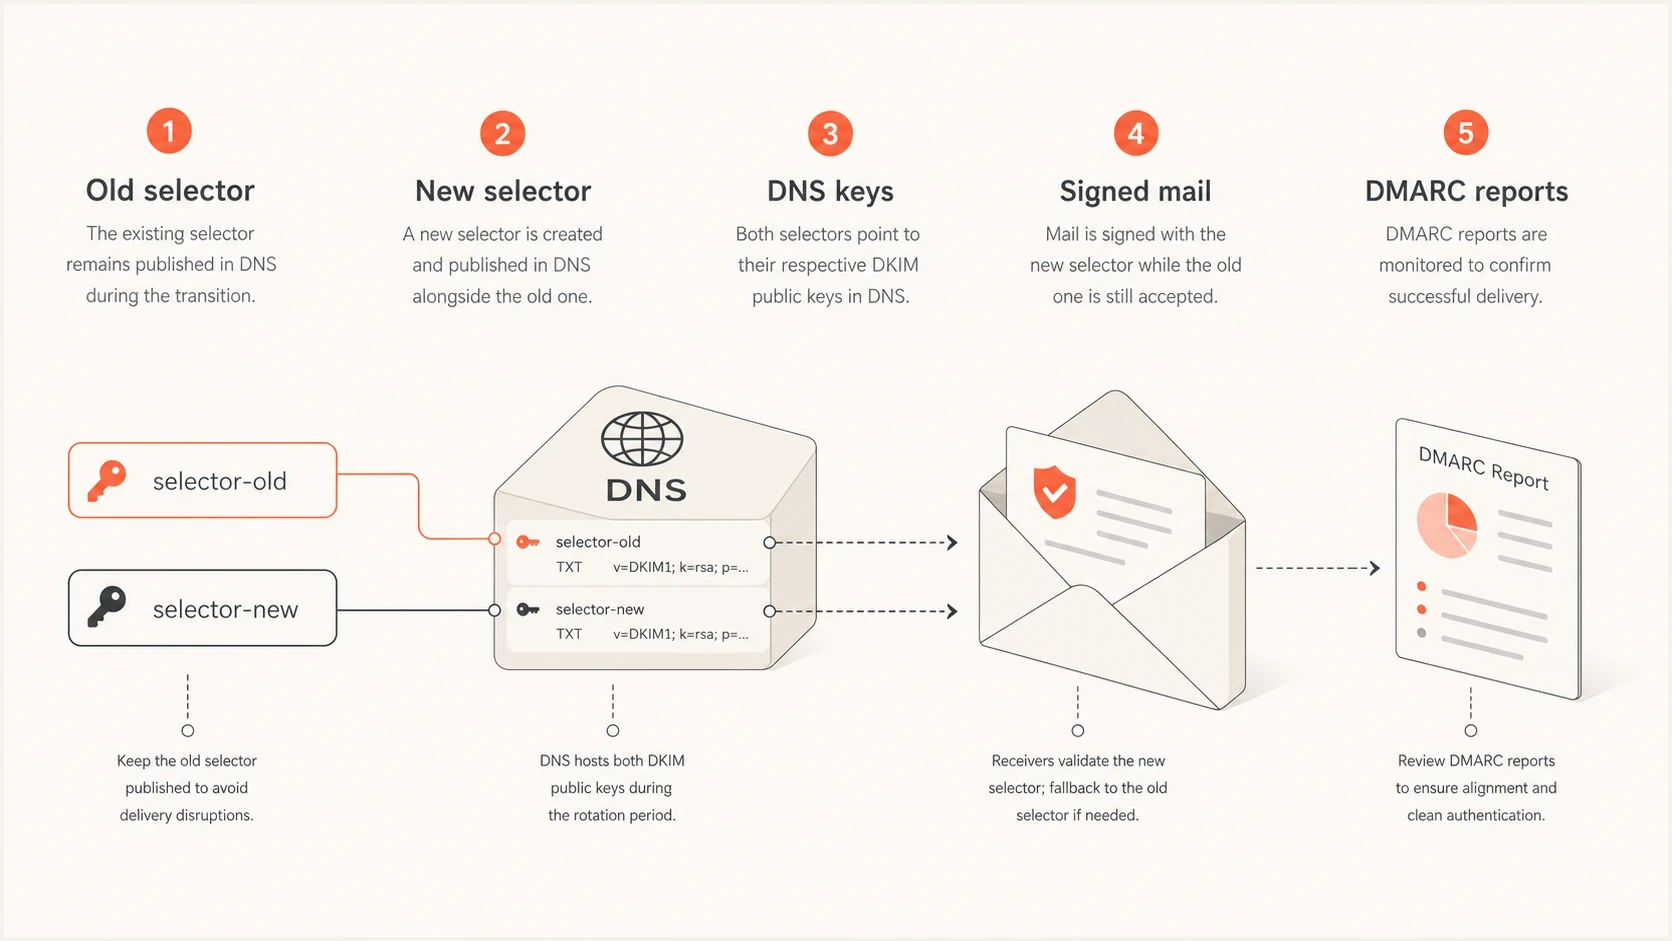
Old and new DKIM selectors connected to DNS keys, signed email, and DMARC reports.
DKIM selectors and signing domain reputation
The signing domain identifies the domain taking responsibility for a DKIM signature. The selector identifies its public key. A new selector under the same signing domain preserves that domain identity. Treat the comparisons below as operational checks, since receivers do not publish a universal reputation-risk scale.
|
|
|
|---|---|---|
Selector | Public key lookup name | New and old signatures verify |
DKIM domain | Signing identity in d= | DMARC domain matching still passes |
Sending IP | Source IP and its sending history | Receiver deferrals and complaints |
From domain | Visible author domain | Authentication and recipient recognition |
What to monitor when a sending identity changes.
Leaving a DKIM key untouched forever is not a safe response to rotation risk. If an old private key leaks, someone can sign mail that verifies against the still-published public key. They do not need access to the domain's DNS or current mail platform. Key rotation shortens that exposure and makes retired access easier to remove.
A valid DKIM signature proves the message was signed with a matching private key. It does not prove the message was authorized by the current team. Retire unused keys after the validation interval and remove access to their private material.
The safest rotation pattern
Use overlapping selectors so old and new public keys remain available during the cutover. Examples are dkim1 and dkim2, or date labels such as s2026a and s2026b. For self-managed keys, use a fresh selector for each new key pair. Follow the documented rotation process for provider-managed selector pairs.
Recommended rotation stages
A staged rollout reduces DKIM failures during the selector change.
mail signed with new selector
- Inventory: List every platform that signs mail for the domain, its selector, sending domain, owner, and rotation method.
- Generate: Create a new key pair and protect the private key with restricted access. Use RSA-SHA256 with a 2048-bit RSA key where supported. Do not use RSA-SHA1. Add Ed25519-SHA256 alongside RSA only when the signing platform supports it and compatibility has been tested.
- Publish: Publish the new public key in a TXT record, or publish a CNAME pointing to a provider-managed key, before changing signing behavior. A selector name change without a new key pair does not rotate the key.
- Validate: After DNS checks pass, test the new selector on a controlled mail stream or with double signing. Confirm DKIM pass and DMARC domain matching, then switch every production signer to the new selector.
- Retire: Retire the old self-managed selector only after every signer has switched and the validation interval has elapsed. Keep selector records required by an active provider-managed rotation process.
Example old and new DKIM selectorsdns
dkim1._domainkey.example.com.  TXT  "v=DKIM1; k=rsa; p=OLD_KEY"
dkim2._domainkey.example.com.  TXT  "v=DKIM1; k=rsa; p=NEW_KEY"
DKIM checker
Check selector records and public key configuration.
?/7tests passed
DNS validation is only the first check. After the record is valid, send real mail through each source and inspect the DKIM-Signature and receiver-added Authentication-Results headers. RFC 8301 specifies RSA key sizes and prohibits RSA-SHA1.
DNS TTL and rollback planning
DNS propagation is part of the rotation window. Record the current TTL before the change. If faster recovery is required, lower the TTL at least one full existing TTL in advance, publish the new selector, and confirm that authoritative and recursive lookups return the complete public key before switching production signing. For a new selector, account for cached NXDOMAIN or no-data responses; lowering the new record's TTL does not shorten an earlier negative-cache entry.
- Preflight: Confirm the new selector resolves through more than one recursive path and matches the private key on the signer.
- Rollback: Keep the old private key secured and the old public key published until the new selector passes on every sending source.
- Decision point: Switch back only when the old key is still trusted. Never restore a private key that is suspected or known to be compromised.
- Emergency: Stop signing with the exposed key immediately. Switch to a trusted, validated replacement, and revoke the exposed public key with an empty p= value or remove its record. For delegated CNAME keys, coordinate revocation with the provider.
Lowering TTL does not flush records already cached under the previous TTL. Make that change before the maintenance window, not at the moment of cutover. Cached public keys can also delay the effect of revocation until their TTL expires.
Why new selectors are safer than reuse
Rotating the key without changing the selector means replacing the TXT value at the same DNS name. It can work if sending stops, old signed messages and queues clear, DNS caches expire, the TXT value changes, and signing resumes only after validation. That sequence is rarely practical for continuous production mail.
Same selector
- Failure window: Old messages can fail after DNS points to the new public key.
- Queue issue: Delayed mail, retries, and forwarded copies can verify later.
- Rollback: Reverting DNS can break mail signed during the attempted change.
New selector
- Parallel keys: Old and new public keys can coexist during the transition.
- Clean cutover: New mail uses the new selector while old mail still verifies.
- Clear audit: Message headers identify the selector directly; DMARC reports provide selector detail when the receiver includes it.
The reason is mechanical. A DKIM signature contains the selector used at signing time. If that message was signed with the old private key, but the public key at the selector now contains the new key, verification fails. RFC 6376 recommends assigning new keys to new selectors.
Selector inside a DKIM signaturetext
DKIM-Signature: v=1; a=rsa-sha256; d=example.com; s=dkim1;
 h=from:subject:date:message-id; bh=...; b=...
Retention and monitoring
No DKIM standard sets a fixed old-selector retention period. M3AAWG key rotation guidance recommends keeping the previous public key available for at least seven days and up to 30 days. Start the interval after the last message signed with the old key. Extend it when actual queue delays or deferred verification require longer; sending volume alone does not determine the interval.
Old selector retention checks
Apply these checks to planned self-managed rotation. Compromised keys require immediate incident handling.
Published guidance
7-30 days
M3AAWG recommends this overlap; it is not a DKIM protocol deadline.
Start of overlap
Last old-key signature
Confirm that every signer has stopped using the old private key.
Retirement check
Queues and checks clear
Allow delayed validation and report delivery to clear before retiring the old key.
If a private key is known to be compromised, treat it as an incident. Stop signing with it, revoke or remove its public key, publish an emergency selector, and review DMARC data for unexpected signed sources. The security risk outweighs preserving verification for messages signed with the exposed key.
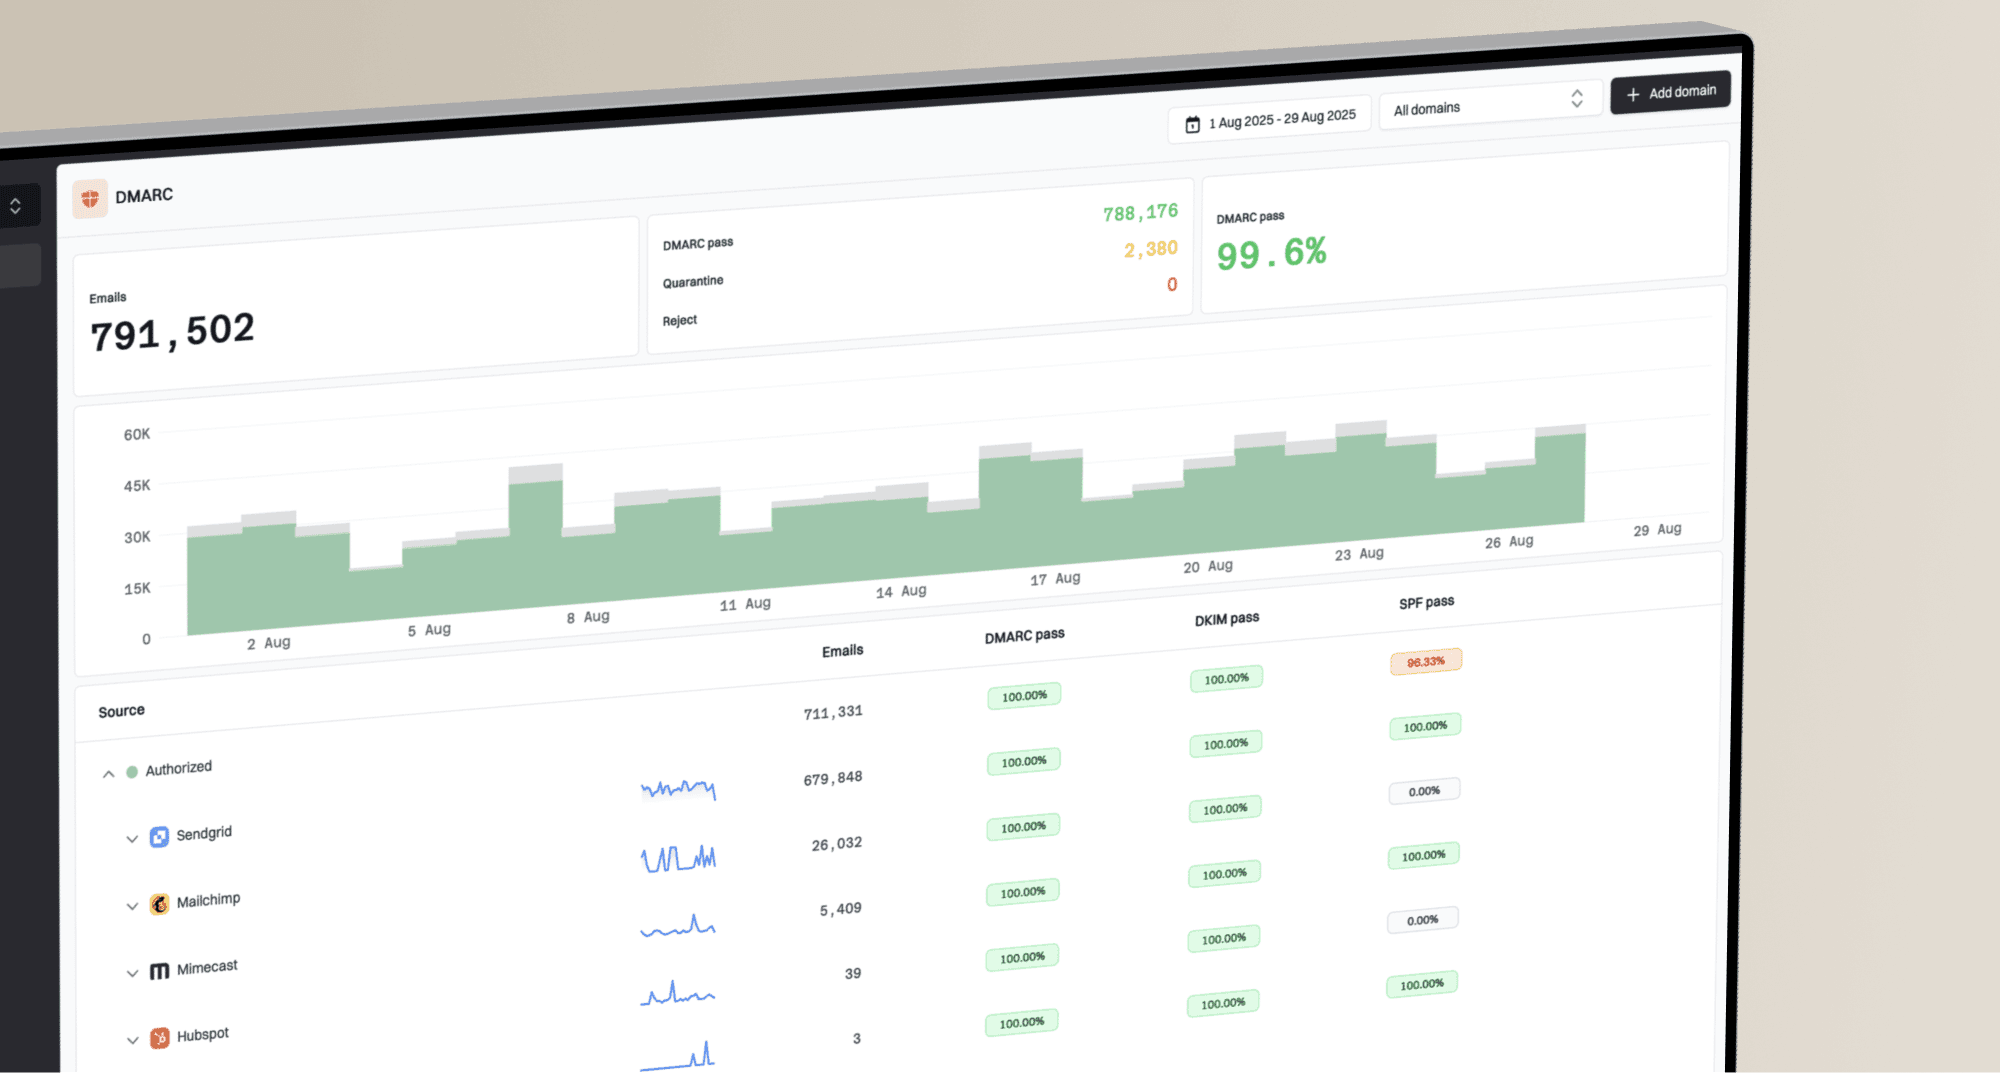
Suped's DMARC monitoring shows sending sources and their authentication results, helping compare the baseline with post-rotation reports. Add the domain to DMARC monitoring before the rotation. Aggregate reports usually arrive daily and are not live telemetry. Use message headers and signer logs for immediate cutover checks.
Suped DMARC dashboard showing email volume, authentication health, and source breakdown
What to check during the change
A rotation needs a before-and-after view. Capture normal DKIM pass rate, DMARC pass rate, source inventory, receiver results, complaints, deferrals, bounces, and SMTP response codes. After the switch, compare those metrics by source and receiver instead of relying on one average.
- Headers: Inspect real test messages and confirm the expected selector, signing domain, algorithm, and Authentication-Results value.
- DNS: Use a DKIM checker to confirm the complete public key is reachable and valid.
- Reports: Review DMARC aggregate data by source and receiver. Check report date ranges and allow delivery lag before concluding that old-selector activity has stopped; confirm this against signer logs.
- Fallback: SPF satisfies DMARC only when its authenticated domain passes the required From-domain matching. Forwarding often breaks SPF, and some receiver requirements still require DKIM, so repair broken DKIM promptly.
RFC 9990 requires selector information for reported DKIM signatures. Legacy or incomplete reports still omit it, and aggregate reports do not cover every receiver. Missing old-selector entries alone do not prove retirement is safe.
?
What's your domain score?
Deep-scan SPF, DKIM & DMARC records for email deliverability and security issues.
A broad domain health check helps when the change touches more than DKIM. Rotation incidents can also expose SPF lookup issues, DMARC domain mismatch, or a forgotten sender.
Selector names and rotation cadence
Selector names should be simple and unique within the signing domain. Avoid account IDs or sensitive internal details. Give independent sending services separate selector namespaces so one key can be rotated or revoked without affecting another service. Date-based selectors make audits easier. Keep fixed selector pairs when the provider requires them; do not overwrite an active selector with a different key. Publish one DKIM key record per selector hostname, with long TXT values split into strings within that same record.
|
|
|
|
|---|---|---|---|
Provider-managed pair | dkim1 / dkim2 | Managed rotation | Keep required records |
Date | s2026a | Audit | More labels |
Provider | s1 | Hosted | Provider controlled |
Common selector naming patterns.
For more examples, this page on selector names is useful. If you are also changing key size, review secure key length before publishing the new record.
No RFC mandates one rotation interval. M3AAWG recommends rotation at least every six months. Use that as a documented baseline for self-managed keys, or follow the hosted provider's supported process. Rotate immediately after suspected compromise and revoke a departing vendor's signing access when the relationship ends.
Double signing and CNAME selectors
Double signing puts two DKIM signatures on a message, often one old selector and one new selector. It is useful when the MTA supports it and the team needs proof that the new selector works on real traffic before relying on it fully. It also supports an RSA-to-Ed25519 transition because each algorithm must use a different selector. Inspect the result of each signature separately: a DMARC pass carried by the old signature does not prove the new signature works. For broad compatibility during an algorithm transition, keep RSA alongside Ed25519 on a separate selector.
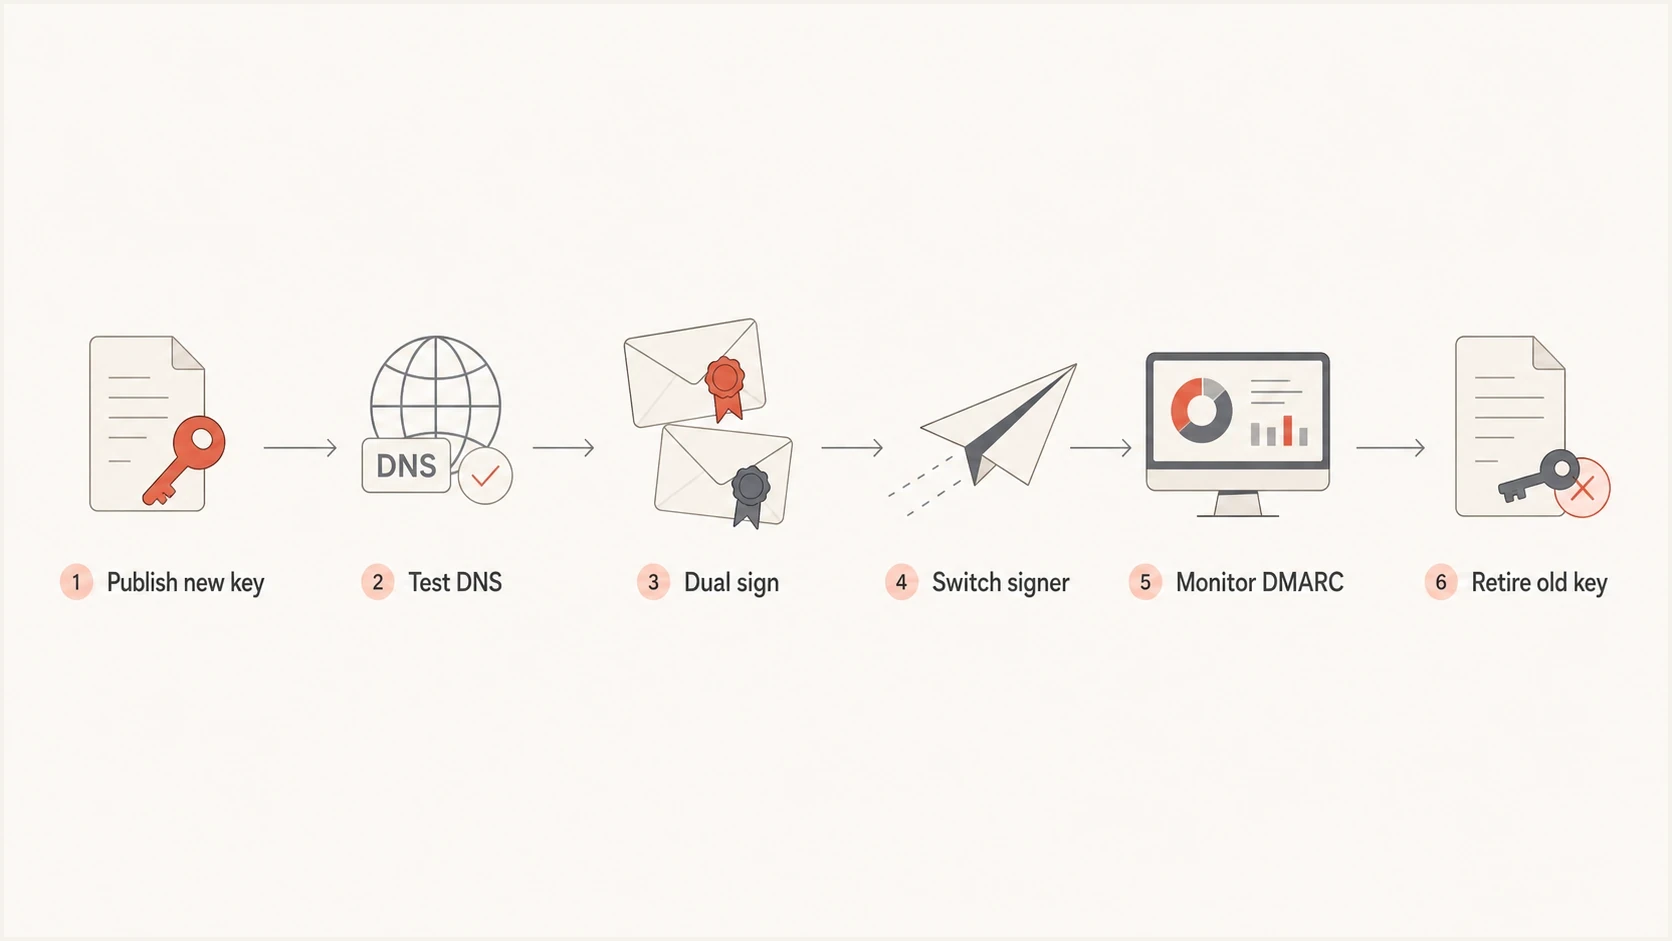
DKIM key rotation steps: publish a new key, test DNS, dual sign, switch signing, monitor, and retire the old key.
CNAME-based DKIM is common with hosted providers. You publish a selector that points to the provider's DNS, and the provider manages the target key material. Keep every CNAME required by the provider, including an inactive selector reserved for later rotation. Do not delete that CNAME after a cutover. Follow the CNAME chain to confirm that the target TXT key resolves, and remove delegated access when the provider relationship ends. Use double DKIM signing when supported to test the new signature before relying on it.
Example provider-managed DKIM CNAMEdns
s1._domainkey.example.com.  CNAME  s1.example.provider-dkim.net.
s2._domainkey.example.com.  CNAME  s2.example.provider-dkim.net.
RFC 8463 describes using separate selectors for RSA and Ed25519 signatures during an algorithm transition.
How to diagnose DKIM failures after rotation
Start with a failing message's DKIM-Signature and the receiving system's Authentication-Results. Use its exact signing domain and selector for the DNS lookup, then compare the result with the signer configuration. A valid DNS record alone does not prove that the production signer used the matching private key.
|
|
|
|---|---|---|
Public key not found | Wrong selector hostname, cached negative answer, or broken CNAME target | Publish the exact record required by the signature and wait for relevant caches to expire. |
Key syntax error | Truncated public key, conflicting key records, or incorrect TXT splitting | Publish one complete key record and verify the DNS response. |
Temporary DNS error | Lookup timeout or failing authoritative DNS | Restore reliable DNS resolution and retest through another recursive resolver. |
Signature or body hash mismatch | Wrong private key or signed content modified after signing | Check the signer's key and any gateway that rewrites signed content. |
Checks for common post-rotation DKIM symptoms.
If DKIM passes but DMARC fails, check the signing domain against the visible From domain under the configured DMARC mode. If authentication stays healthy while delivery worsens, compare complaints and sending patterns before attributing the change to the selector. These checks apply DKIM verification rules in RFC 6376.
Mistakes to avoid
Authentication failures after a selector change need investigation before they are attributed to reputation. If the team changes the selector, IP, From domain, template, audience, and volume in one window, isolating the cause becomes difficult.
- Missing DNS: The MTA signs with a selector before the public key is resolvable.
- Selector conflict: Two active systems use one selector with different private keys, so one of them cannot validate.
- Domain mismatch: The new signer uses a DKIM domain that does not match the visible From domain for DMARC.
- Early cleanup: The old selector is deleted before older messages have finished verifying.
- Bulk changes: The rotation happens during a volume spike, new audience launch, or infrastructure move.
Suped's DMARC monitoring compares authentication and domain-matching results for each sending source. Use those results to identify affected sources, then compare message headers and signer logs with the rotation record to establish whether the selector change caused the failure.
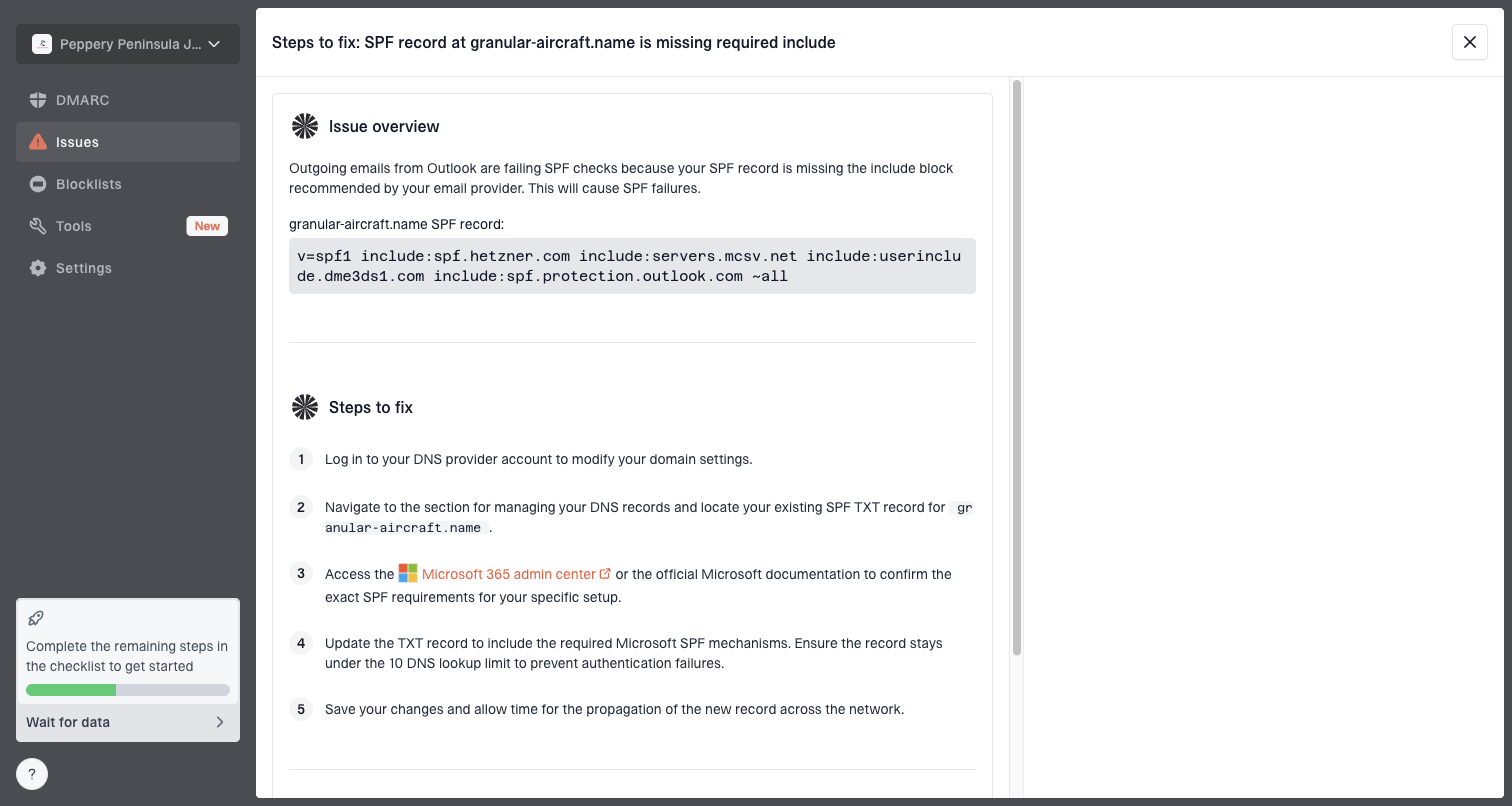
Issue steps to fix dialog showing the issue overview, tailored fix steps, and verification action
Frequently asked questions
A selector-only change normally preserves domain reputation because the signing domain stays the same. Receiver filtering models are proprietary, so identical inbox placement is not guaranteed. No new domain or IP warm-up is needed solely for a selector change.
Yes, but it creates a verification risk for continuous sending. Messages signed before the DNS change can fail after the same selector points to a new public key. A new selector lets both keys coexist.
There is no protocol-mandated period. M3AAWG recommends retaining the previous public key for at least seven days and up to 30 days after its last use. Extend this for delayed verification. Keep CNAME selector records required by an active provider-managed rotation process.
Use RSA-SHA256 with a 2048-bit RSA key where supported. RFC 8301 sets 1024 bits as the RSA minimum and recommends at least 2048 bits; RSA-SHA1 is prohibited. Ed25519-SHA256 is standardized. For broad compatibility, use it alongside RSA with a separate selector and verify both signatures.
Yes, when the MTA supports it. Check that the new signature passes independently, since the old signature can keep DMARC passing even when the new one fails. Double signing also supports an RSA-to-Ed25519 transition using separate selectors.