Why am I getting a Hotmail SSL error and how do I fix it?
Updated on 20 Oct 2026: We clarified Hotmail TLS diagnostics and Outlook.com settings, and added checks for Microsoft's SMTP certificate-chain change.
A Hotmail SSL error can describe two different failures. In outbound mail-server logs, it usually means the sending server failed the TLS handshake with Microsoft before the message was accepted. In Outlook or another mail app, it usually points to a certificate-name mismatch, incorrect server settings, or a problem on the device or network. Identify where the error appears before changing anything.
For an outbound server error, check the sending server's TLS stack, make sure it offers TLS 1.2 or newer, refresh the CA trust store, and confirm the server uses SMTP STARTTLS on port 25 instead of trying to speak implicit SSL at the beginning of the connection. OpenSSL 1.0.2k belongs to a branch whose public upstream support ended on December 31, 2019. It supports TLS 1.2, so the version string alone does not prove why a handshake failed. Check the negotiated protocol and the OS vendor's support status, along with cipher settings and CA certificates.
Typical error
SSL error: connect failed: protocol error while connected to
hotmail-com.olc.protection.outlook.com (104.47.17.97)
Start with the sending host because this server-side error occurs during SMTP transport. DMARC and DKIM checks need message headers, while SPF uses the sending IP and SMTP identity. A TLS protocol error prevents the encrypted SMTP session from completing, so changing authentication records will not repair the handshake.
If the error appears while adding a Hotmail account to a phone or Outlook app, use the client troubleshooting path below. That problem involves account settings or certificate validation, not direct server-to-server delivery. Microsoft's Outlook connection guide covers related certificate errors when mobile apps connect to Exchange Server; it is not a Hotmail account-settings reference.
If the error appears in Outlook or a mail app
A certificate warning in Outlook, a phone, or another mail app needs a client-side check. Do not use the Microsoft MX host or port 25 as account settings. For a personal Hotmail or Outlook.com account configured manually, use the current mailbox endpoints. Outlook.com requires OAuth2 or Modern Auth, so use an app that supports it.
Try signing in to Outlook.com in a browser and check Microsoft's service status before rebuilding an account. If webmail works but the mail app fails, focus on the app settings and its connection path. A browser certificate warning also needs investigation; do not bypass it.
|
|
|
|
|---|---|---|---|
IMAP incoming | outlook.office365.com | 993 | SSL/TLS |
POP incoming | outlook.office365.com | 995 | SSL/TLS |
SMTP outgoing | smtp-mail.outlook.com | 587 | STARTTLS |
Current manual settings for personal Hotmail and Outlook.com accounts
Microsoft's Outlook.com server settings confirm the endpoints above. POP and IMAP access are disabled by default. For a manual POP/IMAP setup, enable the required protocol under Settings > Mail > Forwarding and IMAP, save the change, and use your full Hotmail address as the username. Disabled access or an OAuth2 sign-in failure is separate from a certificate error.
- Check the certificate: Compare the certificate's Subject Alternative Names (SANs) with the configured server name and check its validity dates. Update the app and OS trust store. If the remote certificate is expired, its server administrator must renew it; accepting the warning does not repair it.
- Correct the clock: Set the device date, time, and time zone automatically. A wrong clock can make a valid certificate look expired or not yet valid.
- Test another network: Complete any Wi-Fi sign-in page and retry on a trusted connection. A firewall, proxy, or TLS inspection device can present a different certificate.
- Refresh the account safely: Update and restart the app first. For a recurring 'Cannot verify server identity' warning naming m.hotmail.com, back up local-only mail, then re-add the account using the Outlook.com provider option so the app discovers the settings.
If the certificate names a firewall, proxy, security appliance, or unrelated domain instead of Microsoft, stop approving the warning. Ask the network administrator or email provider to correct the interception or certificate configuration.
Why Hotmail SMTP TLS handshakes fail
When you send directly to a Hotmail or Outlook.com address, your mail transfer agent looks up the recipient domain's MX records and connects to Microsoft's protection infrastructure. The example host, hotmail-com.olc.protection.outlook.com, is the route recorded in that log; use the current DNS answer for testing. Microsoft's server advertises SMTP capabilities, your server requests STARTTLS, and both sides negotiate encryption before mail data moves.
If your library offers only old protocols or incompatible ciphers, or uses the wrong SMTP sequence, Microsoft can close the negotiation. Separately, your sending server can reject Microsoft's certificate if its chain is untrusted or its name does not match. Mail logs can label these failures as an SSL error, protocol error, handshake failure, or connect failed message. The term SSL is legacy wording here. Modern mail delivery uses TLS.
TLS version guidance
Use this as a practical baseline for outbound SMTP to major mailbox providers.
Good
TLS 1.2 or TLS 1.3
Use TLS 1.2 as the minimum and negotiate TLS 1.3 when both servers support it.
Deprecated
TLS 1.1
Do not rely on this for current Microsoft mail delivery.
Critical
TLS 1.0, SSLv3, SSLv2
Remove these protocols from production SMTP stacks.
- Old TLS: The sender offers protocols or ciphers Microsoft no longer accepts.
- Old OpenSSL: The library, CA bundle, or OS package is too old for current remote MX behavior.
- Wrong mode: The sender tries implicit SSL on an SMTP port that expects plaintext first, then STARTTLS.
- Enforced TLS: MTA-STS or a destination-specific policy blocks delivery when TLS or certificate validation does not meet the required policy.
How to diagnose a Hotmail SMTP TLS error
Do not start by changing DMARC records or sender reputation settings. First prove whether the sending server can complete a clean SMTP STARTTLS session to Microsoft. Run the check from the actual sending host or a host with the same mail server, OpenSSL package, firewall route, and outbound policy. Look up the current MX for the recipient domain rather than pinning the hostname or IP in an old error message.
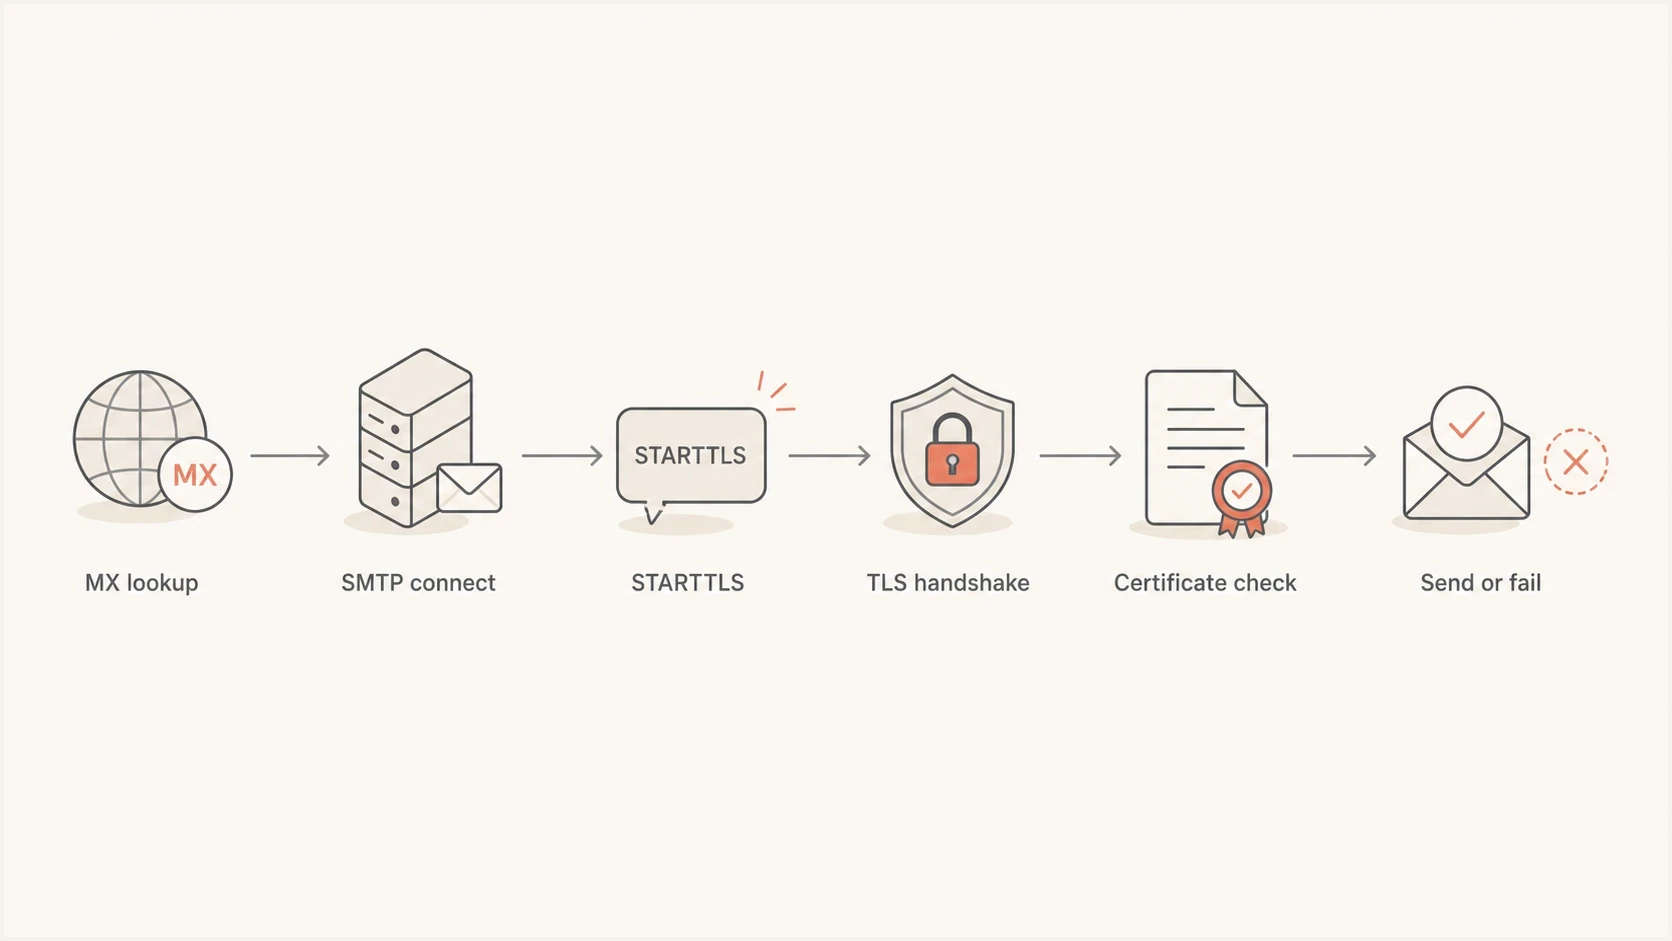
Hotmail SMTP TLS troubleshooting flowchart covering MX lookup, STARTTLS, the handshake, certificate validation, and delivery.
Look up and probe Hotmail's current MXbash
dig +short MX hotmail.com

# Replace this hostname if the current MX lookup differs.
MX_HOST=hotmail-com.olc.protection.outlook.com
openssl s_client -starttls smtp \
  -connect "${MX_HOST}:25" -servername "${MX_HOST}" \
  -tls1_2 -showcerts -verify_return_error \
  -verify_hostname "${MX_HOST}"
A successful probe reports TLS 1.2, a selected cipher, and 'Verify return code: 0 (ok)'; hostname verification uses the MX name supplied above. The -tls1_2 option tests TLS 1.2 specifically. Remove it to test normal version negotiation. Match the mail process's CA bundle with -CAfile when it differs from the command-line default, including inside a container.
A timeout before the SMTP greeting points to connectivity, port 25 filtering, or the remote service. No STARTTLS capability points to the endpoint or SMTP inspection. Certificate verification errors point to the presented chain, trust store, name, or clock. Other handshake errors need the TLS alert and negotiated parameters from the logs. The stage narrows the investigation but does not identify the cause by itself.
|
|
|
|---|---|---|
Protocol | No TLS 1.2 | Upgrade TLS |
Library | Unsupported OpenSSL | Upgrade stack |
Mode | Missing STARTTLS | Use port 25 STARTTLS |
Certificate | Name or chain error | Repair trust checks |
Trust | Old CA bundle | Refresh roots |
Policy | Enforced TLS | Inspect policy maps |
Common checks for Hotmail SMTP TLS errors
Check Microsoft's 2026 certificate-chain change
Microsoft's Exchange Team set March 22, 2026 as the deadline for SMTP systems connecting to Exchange Online to trust DigiCert Global Root G2 and its intermediate CAs. Microsoft's certificate guidance concerns Exchange Online. For a Hotmail error, inspect the chain actually presented by the current MX before attributing the failure to this change.
- If the log says 'unable to get local issuer certificate' or 'certificate verify failed', compare the presented chain with the trust store used by the mail process.
- Update the OS or appliance CA package through its supported update mechanism, including the application or container trust store if it has a separate bundle.
- Confirm that DigiCert Global Root G2 is trusted when the endpoint uses that chain. Keep intermediate certificates in the appropriate intermediate store rather than treating them as trusted roots.
- Restart the affected mail process if required, then repeat the verified STARTTLS probe and retry one queued message.
How to fix the sending server
The direct fix is to modernize the sender, then retest before releasing the queue. Start with the OS packages because the mail server, OpenSSL library, CA store, and cipher defaults are tied together on most Linux systems. Restart the mail service after the upgrade so it loads the new library and trust store.
Postfix 3.6 or newer TLS baseline
smtp_tls_security_level = may
smtp_tls_protocols = >=TLSv1.2
smtp_tls_mandatory_protocols = >=TLSv1.2
smtp_tls_mandatory_ciphers = high
smtp_tls_CAfile = /etc/ssl/certs/ca-certificates.crt
The >=TLSv1.2 syntax requires Postfix 3.6 or newer, as documented in the Postfix TLS parameters. The CA file path shown is common on Debian and Ubuntu; use the path for your OS. smtp_tls_security_level = may is opportunistic: it permits plaintext fallback and does not require a trusted certificate. Keep any existing stronger destination policy. MTA-STS requires separate policy integration; these lines do not enable it. Repair protocol or certificate failures without weakening required TLS checks, and review Microsoft-specific policy maps for stale overrides.
Good repair path
- Upgrade first: Patch the OS, OpenSSL package, mail server, and CA certificates together.
- Retest live: Run an SMTP STARTTLS probe from the same outbound host.
- Drain slowly: Release queued mail in batches and watch for repeat failures.
- Keep logs: Record protocol, cipher, remote MX, and error text for each failure.
Risky repair path
- Disable TLS: Turning encryption off hides the fault and weakens mail transport.
- Pin IPs: Microsoft MX IPs change, so IP pinning breaks again later.
- Ignore CA: Skipping certificate validation removes a useful safety check.
- Patch blind: Changing many mail settings at once makes the real fix harder to prove.
OpenSSL 1.0.2k is a library version, not a TLS protocol version. The live protocol, cipher, and certificate result show what the mail server actually negotiated. Plan migration to a supported stack, and verify any OS vendor maintenance rather than judging support solely by the version string.
Where MTA-STS and DNS fit
MTA-STS applies to server-to-server delivery. A receiving domain publishes a policy. In enforce mode, a sending MTA that supports MTA-STS requires TLS, validates the receiving certificate, and checks the permitted MX hosts. Testing mode reports policy failures without requiring delivery to stop. MTA-STS does not control Outlook sign-in, a phone's mailbox connection, or authenticated SMTP submission on port 587.
If the recipient has a valid enforce policy, failed TLS, certificate, or MX validation prevents delivery through a noncompliant connection. The sender normally queues and retries the message; persistent failure eventually produces a bounce when its queue lifetime expires. RFC 8461 defines this behavior. Repair the failure without bypassing the policy. For domains you own, Suped's Hosted MTA-STS provides a managed way to publish and stage an inbound policy with two CNAME records and no separate policy web host.
Hosted MTA-STS/TLS-RPT configuration dialog showing policy mode, MX hosts, CNAME records, TLS reporting, and verification
Suped's hosted MTA-STS product can pair an inbound policy with TLS-RPT reporting. Use reported certificate and policy failures to investigate deliveries to domains you own. Reports collected for your domain concern inbound delivery; outbound Hotmail errors still require the sending MTA's logs.
Before changing DNS, check the domain's authentication and transport posture with Suped's domain health checker. It helps separate DNS authentication issues from SMTP transport problems so you do not fix the wrong layer.
?
What's your domain score?
Deep-scan SPF, DKIM & DMARC records for email deliverability and security issues.
TLS errors versus authentication and reputation failures
A Hotmail SSL protocol error differs from a DMARC rejection, SPF or DKIM failure, spam placement, or blocklist (blacklist) listing. Read the actual SMTP response: IP reputation checks can happen at connection time, so an early disconnect alone does not prove a TLS fault. A TLS alert or certificate verification error gives a more specific transport diagnosis.
A clean fix has two proofs: your server negotiates TLS 1.2 or newer with Microsoft, and the queued message is accepted by the remote MX. After that, check authentication results and delivery placement as separate follow-up work.
If the message still fails after the TLS fix, read the new SMTP response carefully. A new error such as sender authentication failure, recipient rejection, rate limiting, or reputation filtering means you have moved past the SSL problem into a different delivery issue. Do not keep editing TLS settings once the handshake succeeds.
- Queue ID: Track one failing message through the logs before and after the change.
- Remote MX: Confirm the failing host is still a Microsoft mail endpoint.
- Protocol: Record the negotiated TLS version and cipher after the repair.
- Result: Separate handshake success from the receiving MX accepting responsibility for the message.
Views from the trenches
Best practices
Check the live TLS version from the sending host before changing DNS or policy records.
Keep the mail server, OpenSSL package, and CA trust store patched before rerouting.
Use STARTTLS on SMTP ports, then verify the negotiated cipher in the logs after restart.
Treat repeated Hotmail TLS failures as transport faults before reputation issues.
Common pitfalls
Reading an OpenSSL version as the negotiated TLS version leads to the wrong fix.
Disabling TLS hides the error and weakens transport security for outbound mail delivery.
Changing DMARC policy first wastes time when the SMTP handshake never completes.
Pinning a Microsoft MX IP creates fragile routing because endpoint IPs can change.
Expert tips
Test with the same outbound route because firewalls can alter TLS negotiation results.
Document protocol, cipher, certificate result, and remote MX for every retry attempt.
Release queued mail slowly after repair so repeat errors are easy to isolate quickly.
Review strict TLS policies when one provider starts failing while others still pass.
Marketer view
Marketer from Email Geeks says the TLS version should be checked first because the failure happens before normal message handling.
2022-09-16 - Email Geeks
Marketer view
Marketer from Email Geeks says an old TLS library can fail when Microsoft's mail edge refuses an insecure negotiation.
2022-09-16 - Email Geeks
How to confirm the fix
For a server-side Hotmail SSL error, confirm that the sending host negotiates TLS 1.2 or newer, completes certificate checks required by its policy, and receives a 250 response after the message DATA is complete. An earlier 250 response to EHLO or RCPT TO is not message acceptance. For a client-side error, confirm that the certificate is valid for the configured server and that the app can send and receive without warnings.
Frequently asked questions
Usually, no. A server-side Hotmail SSL error normally happens during SMTP TLS negotiation, before DMARC evaluation. Fix the transport connection first, then review DMARC, SPF, and DKIM if Microsoft accepts the message but delivery still fails.
It can contribute to failures, but 1.0.2k supports TLS 1.2. Public upstream support ended on December 31, 2019. Check the OS vendor's maintenance status and the live handshake results, then plan migration to a supported stack. An old CA bundle or restrictive cipher configuration also needs attention.
No. Disabling TLS hides the fault and weakens transport security. Upgrade the TLS stack, use STARTTLS correctly, and confirm the sender can negotiate TLS 1.2 or newer with Microsoft.
Many mail logs and apps still use SSL as a generic label for encrypted transport. Modern server-to-server SMTP uses TLS through STARTTLS, while IMAP and POP account settings can label their encryption as SSL/TLS.
An enforce policy prevents delivery through an MX connection that fails TLS, certificate, or MX validation. The sending MTA normally queues and retries the message, then bounces it if the problem persists until queue expiry. Testing mode does not require blocking delivery. MTA-STS does not cause certificate warnings inside a mail app.
Use outlook.office365.com with port 993 and SSL/TLS for IMAP, or port 995 and SSL/TLS for POP. Use smtp-mail.outlook.com with port 587 and STARTTLS for outgoing mail. OAuth2 or Modern Auth is required. Enable POP or IMAP access in Outlook.com settings when using that protocol.